security-audit (Cloudflare)
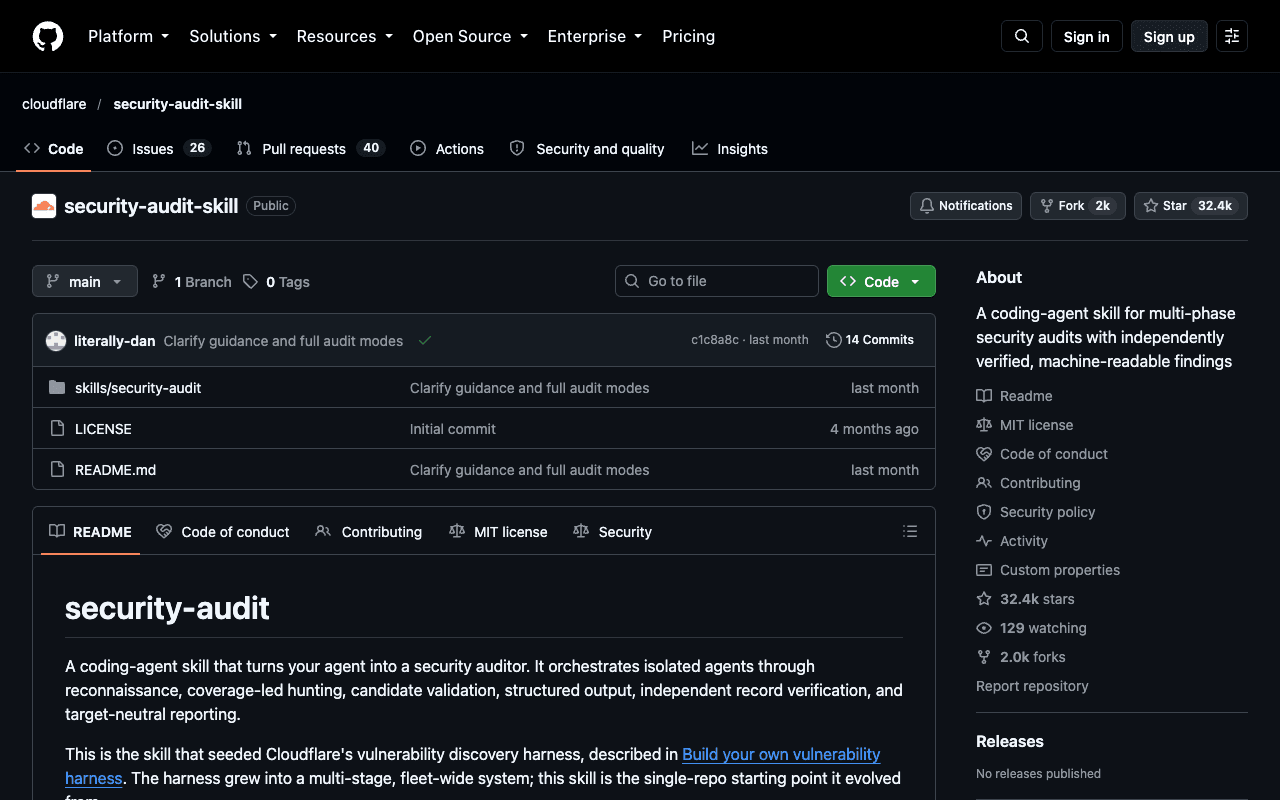
security-audit is a coding-agent skill published by Cloudflare under the MIT license. It orchestrates isolated agents through six phases: reconnaissance, coverage-led hunting, validation of every lead by a verifier that tries to disprove it, structured output, independent verification of the findings, then reporting. Each finding is classed as `confirmed`, `needs_validation` or `rejected`. Cloudflare says this skill seeded its own vulnerability discovery harness. I don't use it on this site: I list it for the rigor of its method.
Key advantages
- Explicit six-phase method: the agent that checks a finding is never the one that found it
- Machine-readable output (`findings.json` validated against a schema) plus Markdown reports
- Unproven leads stay `needs_validation` instead of being declared vulnerabilities
- MIT license, one-command install with the Skills CLI
Who it's for, and why
Developers and security teams who want a first structured audit of a code repository with an agent, and who can review technical findings.
- Running a full security audit of a repository, with a report and detailed findings
- Targeting a specific folder (for example `./src`) for a vulnerability hunt
- Re-running the audit several times on the same repository to widen coverage
Getting started
- 1Install the skill: `npx skills add https://github.com/cloudflare/security-audit-skill --skill security-audit` (add `--global` for a user-level install).
- 2Start the coding agent in the repository to audit (Node.js is required for the validators).
- 3Ask for example: "security audit this codebase"; if you give no output folder, results go to `~/security-audit-skill/<repo-name>/run-<N>`.
Things to watch out for
- Requires a model that supports tool use and parallel sub-agents: not every agent setup qualifies.
- To execute code from the target (builds, tests, fuzzers), the README requires a network-isolated sandbox. Without one, the lead stays `needs_validation` and the code is not run.
- A multi-agent audit is token-hungry: budget for it before running the skill on a large repository.
- A single run is not enough: according to Cloudflare's own tests, it finds roughly half of what repeated runs find.
Frequently asked questions
Does this skill only work with Claude?
No, the README describes a generic coding agent, as long as its model supports tool use and parallel sub-agents. The Skills CLI offers agent-selection options (`npx skills --help`).
Is a `confirmed` finding a certainty?
It rests on a complete source trace and a bounded observed result, checked by an independent agent. It is still an automated audit: a human should review before fixing or communicating.
What does `needs_validation` mean?
A lead backed by the code but with one exact fact still unresolved, often because running it would have required a sandbox. It gets no severity.
Worth exploring too
Claude Code
Anthropic's command-line agent, able to read, write and execute code directly inside a real project.
Vercel MCP
Vercel's MCP server: check deployments, logs and projects directly from an AI agent.
Playwright
Microsoft's browser testing and automation framework, used here to capture real screenshots.